从元旦开始,小家伙就感冒不断,当然,鼻涕也是不停的在流
上次我说过发了风疹块,好象是好了。
前两天,突然又开始感冒,流鼻涕,而且今天身上又开始发小点点。真的不知道是水痘还是别的什么。
皮肤过敏也不能这样吧?难道夏天生的小孩抵抗能力这么差?
唉。希望好起来吧,今天鼻涕已经流了整一天了。看着我非常不开心,不知道他的身体什么时候能够恢复。
算起来,有一个月了呢。
唉。祈祷一下吧。
膘叔的简单人生
从元旦开始,小家伙就感冒不断,当然,鼻涕也是不停的在流
上次我说过发了风疹块,好象是好了。
前两天,突然又开始感冒,流鼻涕,而且今天身上又开始发小点点。真的不知道是水痘还是别的什么。
皮肤过敏也不能这样吧?难道夏天生的小孩抵抗能力这么差?
唉。希望好起来吧,今天鼻涕已经流了整一天了。看着我非常不开心,不知道他的身体什么时候能够恢复。
算起来,有一个月了呢。
唉。祈祷一下吧。
从amr转为mp3并截取过的。。
AMR是手机音乐,下载了:total video converter,先用它把amr转换成MP3
然后用goldwave把Mp3进行了编辑。最后就是这么一小段了。。
因为杂音过多。所以仅保留这段经典的
注:
由于有很多朋友強烈抗議,因此,把自動播放去掉了。請主動點擊。謝謝
一旦點擊就自動循環啦,請仔細聽,歌詞是:我沒有錢,我不要臉。。。
使用THinkPHP框架开发程序,经常容易遗忘的事是什么呢?
1、app runtime没有及时更新
2、datamodel 缓存在更改表结构后没有刷新
3、数据缓存设定的时间太长。而在更改数据后没有主动刷新
4、模版缓存中的 include file 一般不会强制刷新。。
以上是开发注意事情,如果你发现改了一些设置或者其他什么后,死活不正常,请先检查以上四样。
孟宪会友情提醒:注意:以下代码请在Firefox 3.5、Chrome 3.0、Safari 4之后的版本中进行测试。IE8的实现方法与其他浏览不同。
跨域请求,顾名思义,就是一个站点中的资源去访问另外一个不同域名站点上的资源。这种情况很常见,比如说通过 style 标签加载外部样式表文件、通过 img 标签加载外部图片、通过 script 标签加载外部脚本文件、通过 Webfont 加载字体文件等等。默认情况下,脚本访问文档属性等数据采用的是同源策略(Same origin policy)。
那么,什么是同源策略呢?如果两个页面的协议、域名和端口是完全相同的,那么它们就是同源的。同源策略是为了防止从一个地址加载的文档或脚本访问或者设置 从另外一个地址加载的文档的属性。如果两个页面的主域名相同,则还可以通过设置 document.domain 属性将它们认为是同源的。
随着 Web2.0 和 SNS 的兴起,Web 应用对跨域访问的需求也越来越多,但是,在脚本中进行跨域请求是受安全性限制的,Web 开发人员迫切需要提供一种更安全、方便的跨域请求方式来融合(Mashup)自己的 Web 应用。这样做的一个好处就是可以将请求分摊到不同的服务器,减轻单个服务器压力以提高响应速度;另外一个好处是可以将不同的业务逻辑分布到不同的服务器上 以降低负载。
值得庆幸的是,跨域请求的标准已经出台,主流浏览器也已经实现了这一标准。W3C 工作组中的 Web Applications Working Group(Web 应用工作组)发布了一个 Cross-Origin Resource Sharing(跨域资源共享,该规范地址:http://www.w3.org/TR/access-control/和http: //dev.w3.org/2006/waf/access-control/) 推荐规范来解决跨域请求的问题。该规范提供了一种更安全的跨域数据交换方法。具体规范的介绍可以访问上面提供的网站地址。值得注意的是:该规范只能应用在 类似 XMLHttprequest 这样的 API 容器内。IE8、Firefox 3.5 及其以后的版本、Chrome浏览器、Safari 4 等已经实现了 Cross-Origin Resource Sharing 规范,已经可以进行跨域请求了。
Cross-Origin Resource Sharing 的工作方式是通过添加 HTTP 头的方法来判断哪些资源允许 Web 浏览器访问该域名下的信息。然而,对于那些 HTTP 请求导致用户数据产生副作用的请求方法(特别是对于除了GET、某些 MIME 类型的 POST 之外的 HTTP方法),该规范要求浏览器对请求进行“预先验”,通过发送 HTTP 的 OPTIONS 请求头询问服务器有哪些支持的方法,在征得服务器的同意后,再使用实际的 HTTP 请求方法发送实际的请求。服务器也可以通知客户端是否需要将验证信息(如 Cookie 和 HTTP Authentication 数据)随同请求一起发送。
下面我们就采用实际的例子说明 Cross-Origin Resource Sharing 是如何工作的。
1,简单请求
什么样的请求算是简单请求呢?简单请求必须满足下面2点:
a,只使用 GET、POST 进行的请求,这里的POST只包括发送给服务器的数据类型(Content-Type)必须是 application/x-www-form-urlencoded、multipart/form-data 或者 text/plain中一个。
b,HTTP 请求没有设置自定义的请求头,如我们常用的 X-JSON。
先使用下面的代码进行测试:
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN"
"http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<title>孟宪会之AJAX跨域请求测试</title>
</head>
<body>
<input type='button' value='开始测试' onclick='crossDomainRequest()' />
<div id="content"></div>
<mce:script type="text/javascript"><!--
var xhr = new XMLHttpRequest();
var url = 'http://dotnet.aspx.cc/SimpleCrossSiteRequests.aspx';
function crossDomainRequest() {
document.getElementById("content").innerHTML = "开始……";
if (xhr) {
xhr.open('GET', url, true);
xhr.onreadystatechange = handler;
xhr.send();
} else {
document.getElementById("content").innerHTML = "不能创建 XMLHttpRequest";
}
}
function handler(evtXHR) {
if (xhr.readyState == 4) {
if (xhr.status == 200) {
var response = xhr.responseText;
document.getElementById("content").innerHTML = "结果:" + response;
} else {
document.getElementById("content").innerHTML = "不允许跨域请求。";
}
}
else {
document.getElementById("content").innerHTML += "<br/>执行状态 readyState:" + xhr.readyState;
}
}
// --></mce:script>
</body>
</html>
然后,在服务器创建 CrossDomainRequest.aspx 的内容如下:
<%@ Page Language="C#" %>
<mce:script runat="server"><!--
protected void Page_Load(object sender, EventArgs e)
{
Response.AddHeader("Access-Control-Allow-Origin", "http://www.meng_xian_hui.com:801");
Response.Write("孟宪会向各位朋友发来贺电:你的第一个跨域测试成功啦!!!");
}
// --></mce:script>
点击 “开始测试” 按钮,发送的请求和返回的响应信息如下:
GET /SimpleCrossSiteRequests.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
Referer: http://www.meng_xian_hui.com:801/CrossDomainAjax/SimpleCrossSiteRequests.html
Origin: http://www.meng_xian_hui.com:801
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 13:52:00 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Set-Cookie: ASP.NET_SessionId=wk5v5nrs5wbfi4rmpjy2jujb; path=/; HttpOnly
Cache-Control: private
Content-Type: text/html; charset=utf-8
Content-Length: 84
需要特别注意的是:在请求信息中,浏览器使用 Origin 这个 HTTP 头来标识该请求来自于 http://www.meng_xian_hui.com:801;在返回的响应信息中,使用 Access-Control-Allow-Origin 头来控制哪些域名的脚本可以访问该资源。如果设置 Access-Control-Allow-Origin:*,则允许所有域名的脚本访问该资源。如果有多个,则只需要使用逗号分隔开即可。
注意:在服务器端,Access-Control-Allow-Origin 响应头 http://www.meng_xian_hui.com:801 中的端口信息不能省略。
有人可能会想:自己发送请求头会如何呢?比如 xhr.setRequestHeader("Origin","http://www.meng_xian_hui.com:801"); 实践证明,自己设置 Origin 头是不行的。
是不是现在就可以采用 XMLHttpRequest 来请求任意一个网站的数据呢?还是不行的。允许哪些域名可以访问,还需要服务器来设置 Access-Control-Allow-Origin 头来进行授权,具体的代码是:
Response.AddHeader("Access-Control-Allow-Origin", "http://www.meng_xian_hui.com:801");
这行代码就告诉浏览器,只有来自 http://www.meng_xian_hui.com:801 源下的脚本才可以进行访问。
好了,上面我们就完成了一个简单的跨域请求,怎么样?感觉还是不错的吧。下面我们进行一个“预检”请求。
2,预检请求
预检请求首先需要向另外一个域名的资源发送一个 HTTP OPTIONS 请求头,其目的就是为了判断实际发送的请求是否是安全的。下面的2种情况需要进行预检:
a,不是上面的简单请求,比如使用Content-Type 为 application/xml 或 text/xml 的 POST 请求
b,在请求中设置自定义头,比如 X-JSON、X-MENGXIANHUI 等
注意:在 iis 里进行测试,必须在“应用程序扩展”里面配置 .aspx 扩展的动作允许 OPTIONS。
下面我们举一个预检的请求:
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN"
"http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<title>孟宪会之AJAX跨域请求测试</title>
</head>
<body>
<input type='button' value='开始测试' onclick='crossDomainRequest()' />
<div id="content"></div>
<mce:script type="text/javascript"><!--
var xhr = new XMLHttpRequest();
var url = 'http://dotnet.aspx.cc/PreflightedRequests.aspx';
function crossDomainRequest() {
document.getElementById("content").innerHTML = "开始进行请求……";
if (xhr) {
var xml = "<root>测试</root>";
xhr.open('POST', url, true);
xhr.setRequestHeader("POWERED-BY-MENGXIANHUI", "Approve");
xhr.setRequestHeader("Content-Type", "application/xml");
xhr.onreadystatechange = handler;
xhr.send(xml);
} else {
document.getElementById("content").innerHTML = "不能创建 XMLHttpRequest。";
}
}
function handler(evtXHR) {
if (xhr.readyState == 4) {
if (xhr.status == 200) {
var response = xhr.responseText;
document.getElementById("content").innerHTML = "结果:" + response;
} else {
document.getElementById("content").innerHTML = "不能进行跨越访问。";
}
}
else {
document.getElementById("content").innerHTML += "<br/>执行状态 readyState:" + xhr.readyState;
}
}
// --></mce:script>
</body>
</html>
上面的例子我们发送 xml 格式的数据,并且,发送一个非标准的HTTP头 POWERED-BY-MENGXIANHUI 来说明服务器端该如何设置响应头的。
在服务器端,PreflightedRequests.aspx 的内容如下:
<%@ Page Language="C#" %>
<mce:script runat="server"><!--
protected void Page_Load(object sender, EventArgs e)
{
if (Request.HttpMethod.Equals("GET"))
{
Response.Write("这个页面是用来测试跨域 POST 请求的,直接浏览意义不大。");
}
else if (Request.HttpMethod.Equals("OPTIONS"))
{
//通知客户端允许预检请求。并设置缓存时间
Response.ClearContent();
Response.AddHeader("Access-Control-Allow-Origin", "http://www.meng_xian_hui.com:801");
Response.AddHeader("Access-Control-Allow-Methods", "POST, GET, OPTIONS");
Response.AddHeader("Access-Control-Allow-Headers", "POWERED-BY-MENGXIANHUI");
Response.AddHeader("Access-Control-Max-Age", "30");
//此过程无需返回数据
Response.End();
}
else if (Request.HttpMethod.Equals("POST"))
{
if (Request.Headers["Origin"].Equals("http://www.meng_xian_hui.com:801"))
{
System.Xml.XmlDocument doc = new System.Xml.XmlDocument();
doc.Load(Request.InputStream);
Response.AddHeader("Access-Control-Allow-Origin", "http://www.meng_xian_hui.com:801");
Response.Write("您提交的数据是:<br/><br/>" + Server.HtmlEncode(doc.OuterXml));
}
else
{
Response.Write("不允许你的网站请求。");
}
}
}
// --></mce:script>
点击“开始测试”按钮,将会执行下面的一系列请求。
OPTIONS /PreflightedRequests.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
Origin: http://www.meng_xian_hui.com:801
Access-Control-Request-Method: POST
Access-Control-Request-Headers: powered-by-mengxianhui
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 14:00:34 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Access-Control-Allow-Methods: POST, GET, OPTIONS
Access-Control-Allow-Headers: POWERED-BY-MENGXIANHUI
Access-Control-Max-Age: 30
Set-Cookie: ASP.NET_SessionId=5npqri55dl1k1zvij1tlw3re; path=/; HttpOnly
Cache-Control: private
Content-Length: 0
POST /PreflightedRequests.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
POWERED-BY-MENGXIANHUI: Approve
Content-Type: application/xml; charset=UTF-8
Referer: http://www.meng_xian_hui.com:801/CrossDomainAjax/PreflightedRequests.html
Content-Length: 19
Origin: http://www.meng_xian_hui.com:801
Pragma: no-cache
Cache-Control: no-cache
<root>测试</root>
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 14:00:34 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Set-Cookie: ASP.NET_SessionId=byvose45zmtbqy45d2a1jf2i; path=/; HttpOnly
Cache-Control: private
Content-Type: text/html; charset=utf-8
Content-Length: 65
以上的代码反映了预检请求的执行过程:首先发送 OPTIONS 请求头,用来向服务器咨询服务器的更多信息,以便为后续的真实请求做准备。比如是否支持 POST 方法等。值得注意的是:
浏览器还发送 Access-Control-Request-Method: POST 和 Access-Control-Request-Headers: powered-by-mengxianhui 请求头。
注意:以上过程是第一次请求的时候的过程,如果在 30 秒内重复点击按钮,你可以看不到 OPTIONS 这一过程。则执行过程是这样的:
POST /PreflightedRequests.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
POWERED-BY-MENGXIANHUI: Approve
Content-Type: application/xml; charset=UTF-8
Referer: http://www.meng_xian_hui.com:801/CrossDomainAjax/PreflightedRequests.html
Content-Length: 19
Origin: http://www.meng_xian_hui.com:801
Pragma: no-cache
Cache-Control: no-cache
<root>测试</root>
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 14:06:32 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Set-Cookie: ASP.NET_SessionId=qs1c4urxywdbdx55u04pvual; path=/; HttpOnly
Cache-Control: private
Content-Type: text/html; charset=utf-8
Content-Length: 65
为什么会这样?细心的童鞋可能注意到了,在服务器端有一行代码 Response.AddHeader("Access-Control-Max-Age", "30"); 它是用来设置预检的有效时间的,单位是秒。这一点要特别注意。
3,带验证信息的请求
身份验证是Web开发中经常遇到的问题,在跨域请求中,默认情况下是不发送验证信息的。要想发送验证信息,需要进行withCredentials 属性,下面就是一个简单请求的例子:
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN"
"http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<title>孟宪会之AJAX跨域请求测试</title>
</head>
<body>
<input type='button' value='开始测试' onclick='crossDomainRequest()' />
<div id="content"></div>
<mce:script type="text/javascript"><!--
var xhr = new XMLHttpRequest();
var url = 'http://dotnet.aspx.cc/RequestsWithCredentials.aspx';
function crossDomainRequest() {
document.getElementById("content").innerHTML = "开始进行请求……";
if (xhr) {
xhr.open('GET', url, true);
xhr.onreadystatechange = handler;
xhr.withCredentials = "true";
xhr.send();
} else {
document.getElementById("content").innerHTML = "不能创建 XMLHttpRequest。";
}
}
function handler(evtXHR) {
if (xhr.readyState == 4) {
if (xhr.status == 200) {
var response = xhr.responseText;
document.getElementById("content").innerHTML = "结果:" + response;
} else {
document.getElementById("content").innerHTML += "<br/>执行状态 status:" + xhr.status;
}
}
else {
document.getElementById("content").innerHTML += "<br/>执行状态 readyState:" + xhr.readyState;
}
}
// --></mce:script>
</body>
</html>
点击“开始测试”,我们可以检测到下面的请求执行过程:
GET /RequestsWithCredentials.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
Referer: http://www.meng_xian_hui.com:801/CrossDomainAjax/RequestsWithCredentials.html
Origin: http://www.meng_xian_hui.com:801
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 14:12:26 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Access-Control-Allow-Credentials: true
Set-Cookie: ASP.NET_SessionId=fn2zf0zq1cuwgf45fm5fw145; path=/; HttpOnly
Set-Cookie: visit=1; expires=Sun, 10-Jan-2010 14:12:56 GMT; path=/
Cache-Control: no-cache
Pragma: no-cache
Expires: -1
Content-Type: text/html; charset=utf-8
Content-Length: 1
从上面的响应中可以看出,Cookie 是会随请求一起发送的。如果我们多次点击测试按钮,则可以看到请求和响应的结果是这样的:
GET /RequestsWithCredentials.aspx HTTP/1.1
Host: dotnet.aspx.cc
User-Agent: Mozilla/5.0 (Windows; U; Windows NT 5.2; zh-CN; rv:1.9.1.7) Gecko/20091221 Firefox/3.5.7 (.NET CLR 3.5.30729)
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8
Accept-Language: zh-cn,zh;q=0.5
Accept-Encoding: gzip,deflate
Accept-Charset: GB2312,utf-8;q=0.7,*;q=0.7
Keep-Alive: 300
Connection: keep-alive
Referer: http://www.meng_xian_hui.com:801/CrossDomainAjax/RequestsWithCredentials.html
Origin: http://www.meng_xian_hui.com:801
Cookie: ASP.NET_SessionId=fn2zf0zq1cuwgf45fm5fw145; visit=2
HTTP/1.x 200 OK
Date: Sun, 10 Jan 2010 14:13:58 GMT
Server: Microsoft-IIS/6.0
X-Powered-By: ASP.NET
X-AspNet-Version: 2.0.50727
Access-Control-Allow-Origin: http://www.meng_xian_hui.com:801
Access-Control-Allow-Credentials: true
Set-Cookie: visit=3; expires=Sun, 10-Jan-2010 14:14:28 GMT; path=/
Cache-Control: no-cache
Pragma: no-cache
Expires: -1
Content-Type: text/html; charset=utf-8
Content-Length: 1
注意 Cookie: ASP.NET_SessionId=fn2zf0zq1cuwgf45fm5fw145; visit=2 这一行,访问计数器已经被一起发送到服务器。
4,IE8 中的实现方法
IE8已经开始支持跨域访问资源了,但是,IE8提供的功能还比较简单,可以进行简单的请求,下面是一个使用的例子:
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN"
"http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml">
<head>
<title>孟宪会之AJAX跨域请求测试</title>
</head>
<body>
<input type='button' value='开始测试' onclick='crossDomainRequest()' />
<div id="content"></div>
<mce:script type="text/javascript"><!--
var xhr = new XDomainRequest();
var url = 'http://dotnet.aspx.cc/SimpleCrossSiteRequests.aspx';
function crossDomainRequest() {
document.getElementById("content").innerHTML = "开始……";
if (xhr) {
xhr.open('GET', url);
xhr.onload = handler;
xhr.send();
} else {
document.getElementById("content").innerHTML = "不能创建 XDomainRequest";
}
}
function handler(evtXHR) {
document.getElementById("content").innerHTML = "结果:" + xhr.responseText;
}
// --></mce:script>
</body>
</html>
另外,IE8的实现方法与其他浏览器不同。更多内容请参考 XDomainRequest 对象,地址是:
http://msdn.microsoft.com/zh-cn/library/cc288060(VS.85).aspx
最后,愿意测试的朋友可以访问这个 http://dotnet.aspx.cc/SimpleCrossSiteRequests.aspx 地址进行“简单请求”的测试,本页面允许任何地址进行跨域访问。(不好意思,个人网站可能被河蟹了)
----EOF---
很长的文章,我把三篇并为一篇了。。如果嫌长,可以去这里查看 :
AJAX(XMLHttpRequest)进行跨域请求方法详解(一)
google reader恐怕很多人都在用吧。当然在国内也有很多人使用有道的RSS订阅,鲜果的RSS订阅。
不过,我仍然是说的google reader,在我的博客里以前也介绍过。
今天我说的合理使用Google reader,是指另类的用法。
一些技术型 的博客,往往都是在国外,而正常的时候,我们好象都无法访问,怎么办?只能借着偶尔翻墙的时机,订阅那些博客的RSS源。如果你用的是国内的RSS订阅,那么也很有可能是无法订阅的。所以,GoogleReader就派用场了。
再深再远,他都能够帮你订阅回来,只是。。。无法回复而己
借着这个功能,我订阅了几个写mysql proxy的作者的博客。
当然更重要的是,我订阅了twitter上的两位:孙燕姿和萧亚轩。。
所以,懂的喽。。。什么非死不可啦,推特啦,博客班点啦。哈哈。。。都可以尝试订阅你所关注的对象,除了这个嘛。。。。你当然仍然不能回复 。除非你为google reader推插件。。。
如果你用firefox写个插件,或许也能够回复哦?
Debugging your client code is rather a normal procedures for any web developers. Everyone will shout Firebug! yeah, me too. But Firebug is great for syntax detection but how about logic problem? In this article i will share with you some of the ways i used to debug my JavaScript or jQuery codes when I’m developing my web application. I will also share with you a trick that i used on my code to alert me that a bug occurs in a particular script since i don’t get many helpful users nowadays.
The most simple and basic way of debugging is by using JavaScript alert function. This is old but is quite useful sometimes. Especially when you do not want to remember other debugging methods. It’s pretty simple, alert the message you want to see. If the alert doesn’t appear, this means that the error is before the alert statement. I usually do this when I’m debugging IE although there are tools available for IE.
alert("The Bug Is Somewhere Before ME!");Well, if you are using WebKit browsers for your development (FireFox, Chrome, Safari) you may want to try this.
if (window.console)
window.console.log("The Bug is killing me");
What this does is to log the string ‘The Bug is killing me’ into the console such as Firebug. It’s always better than using alert and see this infinity loop that keep popping out until you are force to shut down your browser!
The above two methods work both in jQuery and JavaScript. But this only function well in jQuery. This is definitely not something i came up with but its from Dominic Mitchell
jQuery.fn.log = function (msg) {
console.log("%s: %o", msg, this);
return this;
};
The above creates a function, ‘log’. This function will do exactly similar to the one above but the differences is that it format the string a little bit before displaying out to the console. This is good for debugging your long chaining with jQuery. Although the previous method also can be used to debug chaining but it will required an additional line instead of including it into the chaining process. So you can debug this way,
$(root).find('li.source > input:checkbox').log("sources to uncheck").removeAttr("checked");In JavaScript, you can try to catch the error in a particular scope. This way, it won’t propagate to other section of the code.
try
{
//Run some code here
}
catch(err)
{
//Handle errors here
}
This is pretty good when you are trying to debug one of the many function in your JavaScript.
The last one i am going to show you is to catch any one of the error into a particular function instead of using multiple try and catch.
function handleError(e)
{
alert(’An error has occurred!\n’+e);
return true;
}
window.onerror = handleError;
This will handle any error occurs in your JavaScript code to the function ‘handleError’. You will want to use this at the end of your script. Especially if you want to be informed whether a particular function or script has malfunction and the users are not reporting. Basically, what you can do is to gather all information and placed them into a String or JSON. Using ajax to delivery these information to your email or database. This way, your support team will have an idea which part are having problems and your system will be more reliable. (testing doesn’t means 100% bug free) The information that you may want to know are usually located at Navigator Object in JavaScript.
These are the methods i usually look at when debugging my own client script. It might not be everything but i hope it can be useful to some of you out there. Hope you learn something!
原文来自于:http://hungred.com/2009/08/04/useful-information/ways-debug-jquery-javascript-codes/
互联网时间,每天都有一些新闻啊。
这不,前段时间it168,51,博客大巴刚刚关掉没多久,现在篱笆网也被关掉了。去新网查一下,输入域名:
然后会弹出:
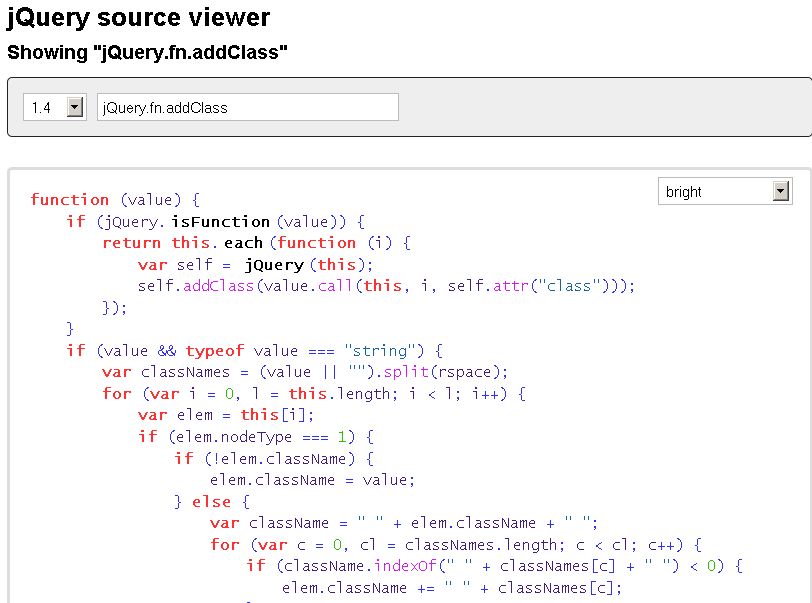
汗死,居然是这种原因。看来举报人或者工信部之类的对于这类事情很痛恨啊。
不过。liba.cn还是可以访问的。。论坛嘛 ,又换了域名了。不知道下一个会是谁去举报。。。真有意思。还好我这里不允许用户输入【是评论都需要审核】
唉。还是审核好啊。天啊,人人自危?
说是万能,意思是他支持多种程序语言。而且调用方式也非常简单,当然官方也有例子
Recaptcha,这是一个验证码程序,其实真的很方便,如果你一天到晚还在为着验证码被别人破解而不停的改进自己的验证码时,你可以用它;如果你不会写验证码程序,你可以用它;如果你想支持语音验证,你也可以用它;如果你想有更多的功能,当然你一样可以用它。
使用方法比较简单,大致如下:
require_once('recaptchalib.php');
$publickey = "..."; // you got this from the signup page,这里就是你刚才申请的API KEY
echo recaptcha_get_html($publickey);
4.In the code that processes the form submission, you need to add code to validate the CAPTCHA. Otherwise, the CAPTCHA will appear, but the answers won't be checked. The validation code looks like:在提交处理页,你需要添加CAPTCHA验证代码。否则,CAPTCHA并不会验证他们。验证代码大致如下:
require_once('recaptchalib.php');
$privatekey = "..."; //申请的API KEY
$resp = recaptcha_check_answer ($privatekey,
$_SERVER["REMOTE_ADDR"],
$_POST["recaptcha_challenge_field"],
$_POST["recaptcha_response_field"]);

if (!$resp->is_valid) {
die ("The reCAPTCHA wasn't entered correctly. Go back and try it again." .
"(reCAPTCHA said: " . $resp->error . ")");
}
看起来是不是很简单?现在是不是不再犹豫了??
更多参考和参数可以查看这里:http://recaptcha.net/plugins/php/
在这次活动中,cssrain属于不幸阵亡的一位。期间问过cssrain的站长,仿佛还是倒在备案和其他问题上。
所幸的是,现在他开通了。别问我为什么,我也不知道,我只是从googlereader里发现了他的博客又能够被google reader看到了而己。
基于这个理由,恭喜一下,祝贺一下。毕竟这也是国内关于jQuery等前端应用博客中还算较有名的一位。

断网,这真的让我很惊讶。我想想我的有线通费用是交到今年6月份的,再加上送的一个月,应该是到7月19日,但事实上,它确实是断了。
打电话 96877,发现是说我09年的有线电视费用没交,一般来说,上海这边有线电视费都是过完年后交的吧?我什么单子和通知都没有收到,就突然的关掉了。
原来机顶盒的功能是这样的呀,以后要当心了。有机顶盒的朋友要注意啊,说不定哪天你想看的电视节目就突然间被停掉了。【机顶盒的功能不是为了让你多看一些电视节目,而是为了让他们方便管理。可恨的是机顶盒需要经常升级,如果你晚上关掉机顶盒,有的时候升级失败的话,你就看不到电视了。只是不知道IPTV是否能看电视,如果能的话,倒情愿装IPTV了。算下来IPTV的费用也和有线通+有线电视费用差不多了】
我继续问,我的有线通费用是交了的呀。他说不行只要有一样停了。那么所有的都要停,我就觉得不可思议了,如果我以后不看电视怎么办?难道网也不让我上了?客服的回答却偏偏 就是这样。如果不用有线电视,那以后也不能用有线通。
让他退款吧。人说现在是停机状态,你只能先去营业厅开通或者做其他处理也行。想想就郁闷 。
有线电视停就停呗,我还能看所谓的6个台的。也够我看了,但你凭什么把我网络也给断了?
莫名其妙
